
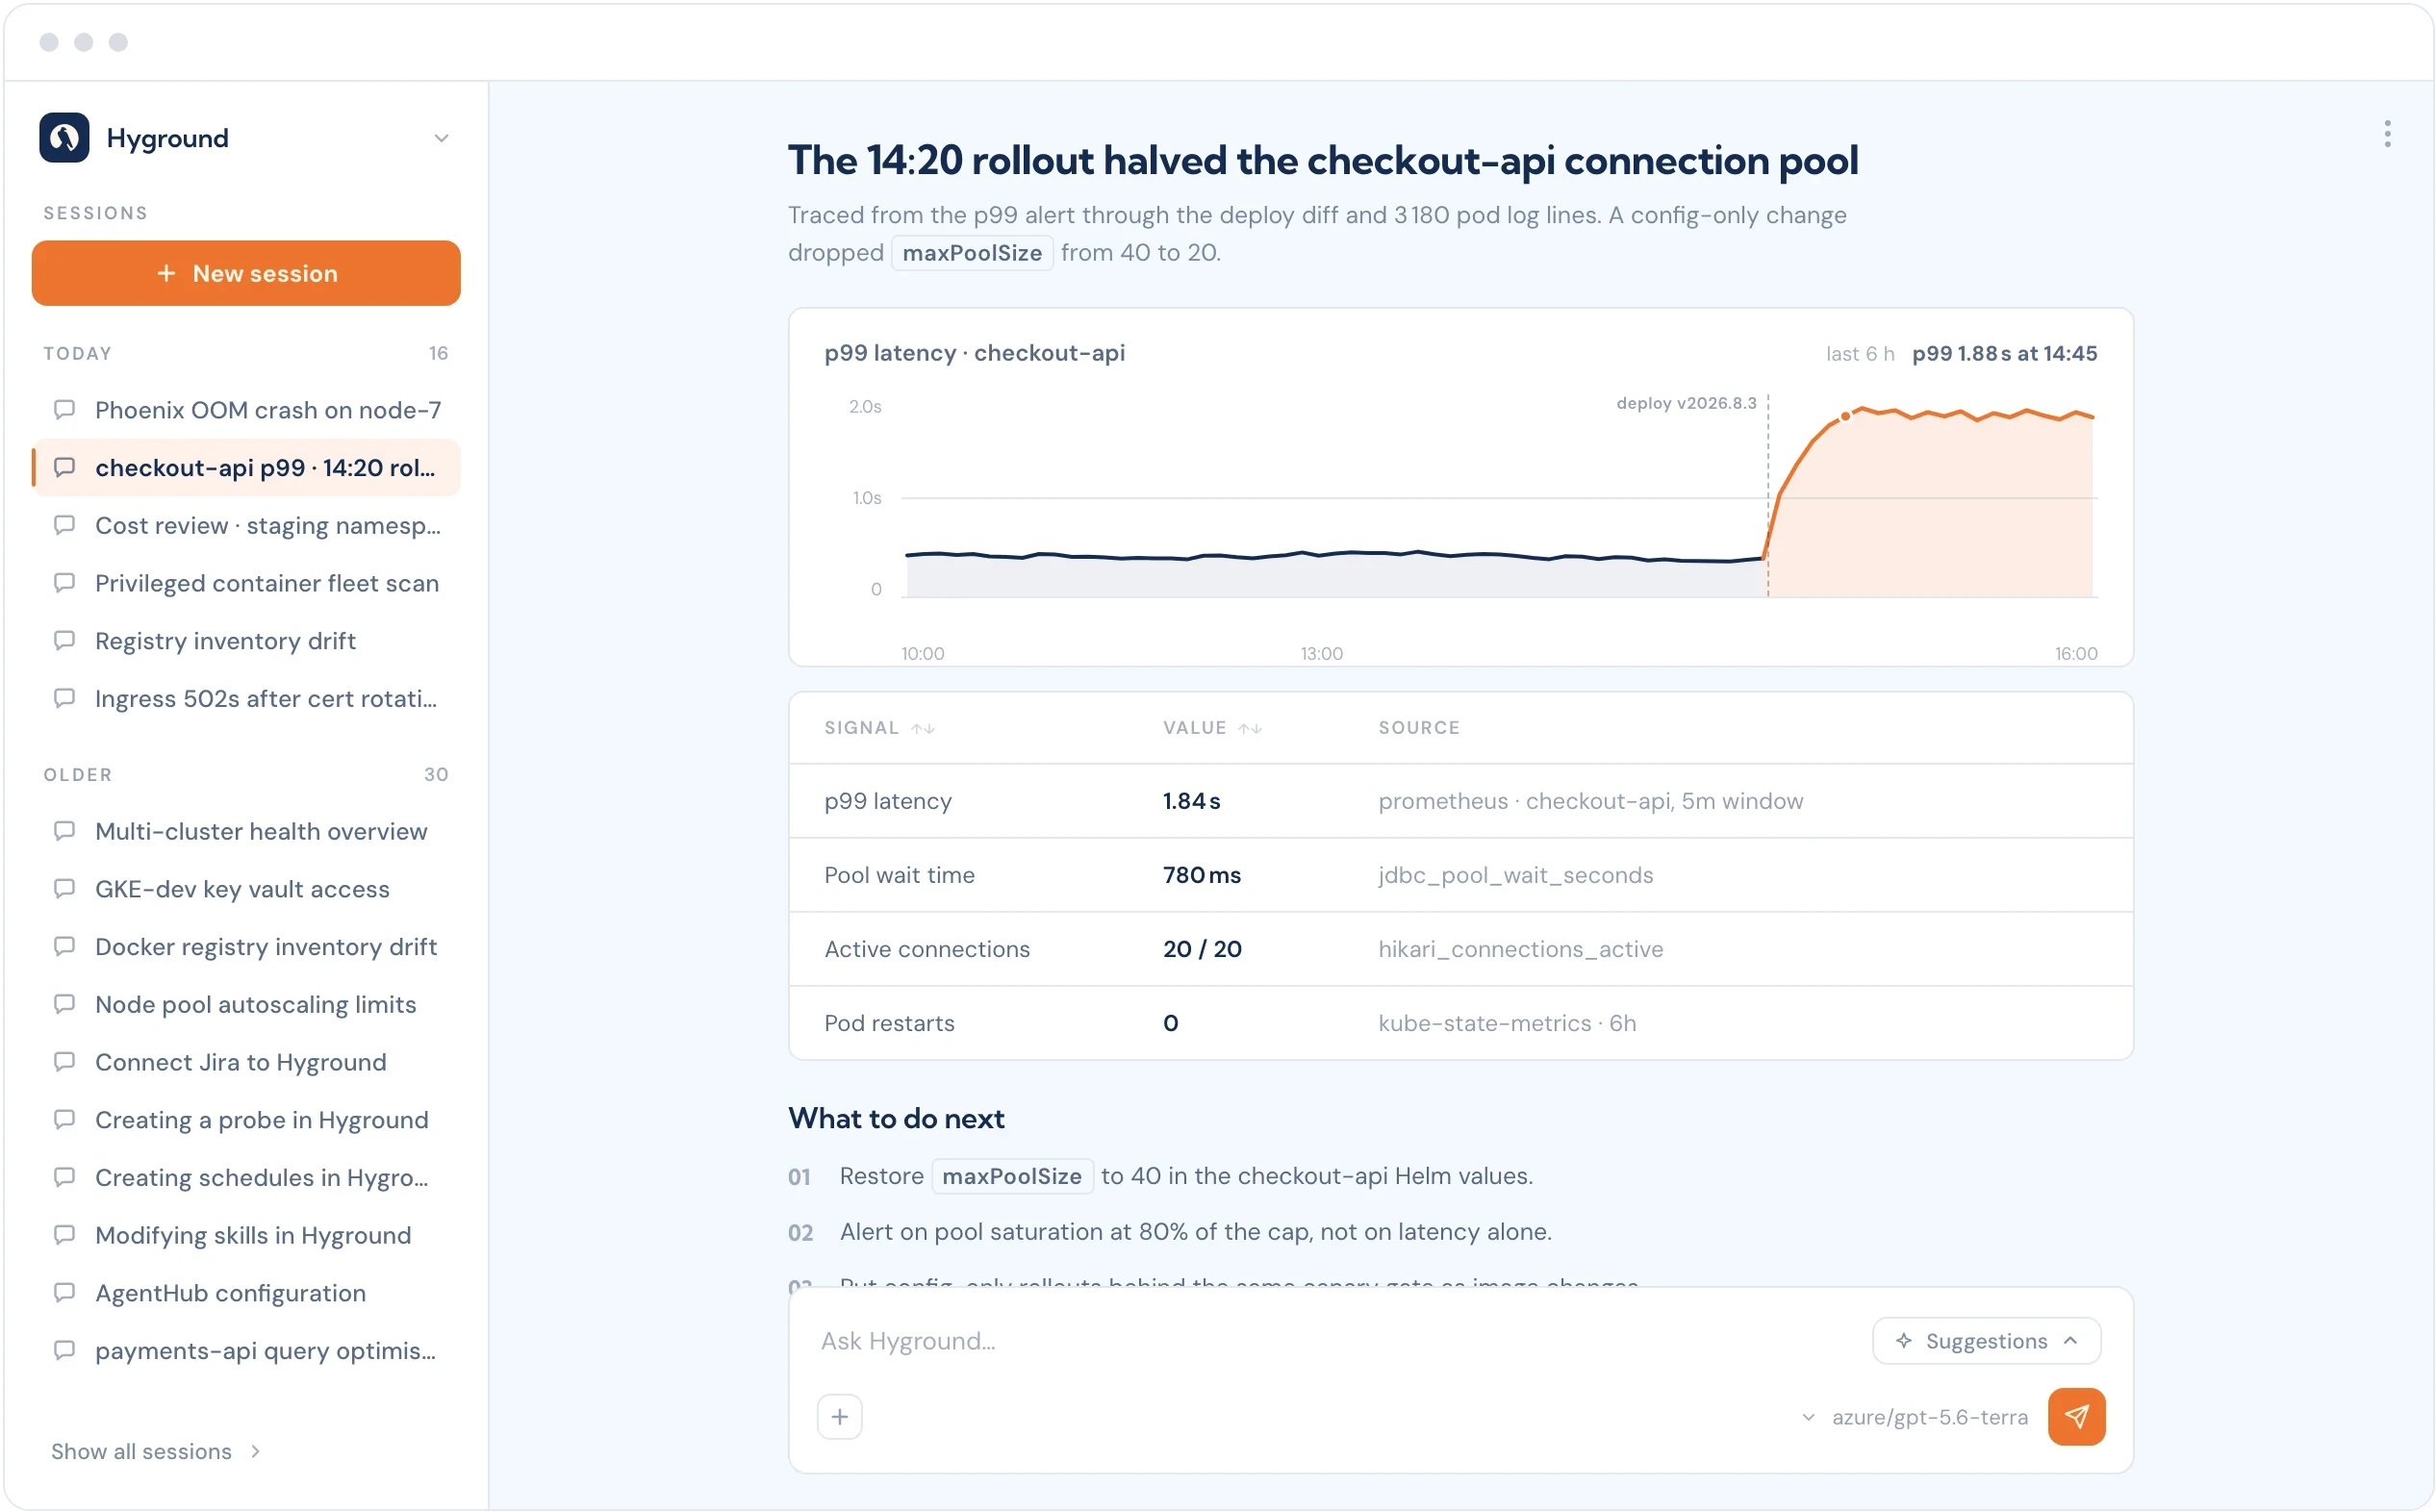
Endless integrations
Integration is the URL, not code
No per-source adapters. Two LLMs (an injection_judge and an alert_extractor) reason over payload semantics, so any new producer is wired up the moment it can POST JSON to /api/herald/webhook. Webhooks, cron jobs, scripts, monitoring stacks, ticket systems, deployment tooling all enter through the same door.
How Hyground protects the webhook endpoint from injection
Every payload needs to pass both gates before a single agent token is spent on it.
Does a trigger call block while the investigation runs?
Webhook callers get a fast acknowledgement, but investigation happens in the background.
Want to go deeper?
Triggers compose with the rest of the platform
An incoming trigger is just an entry point. Once a session is open, every Skill, every connected adapter, every scheduled workflow is available to it.
How the trigger endpoint is authenticated and governed
Herald is the front door. The same governance that applies to any Hyground session applies here: read-only by default, every investigation auditable, every action recommended with evidence to a human in the driver's seat.
The ingress gate decides *who* can post. The semantic gate decides *what* reaches an agent. The session log captures *everything* that happens after.
